|
|
|
0 members (),
2,696
guests, and
28
robots. |
|
Key:
Admin,
Global Mod,
Mod
|
|
S |
M |
T |
W |
T |
F |
S |
|
|
|
1
|
2
|
3
|
4
|
5
|
|
6
|
7
|
8
|
9
|
10
|
11
|
12
|
|
13
|
14
|
15
|
16
|
17
|
18
|
19
|
|
20
|
21
|
22
|
23
|
24
|
25
|
26
|
|
27
|
28
|
29
|
30
|
|
|
|
|
There are no members with birthdays on this day. |
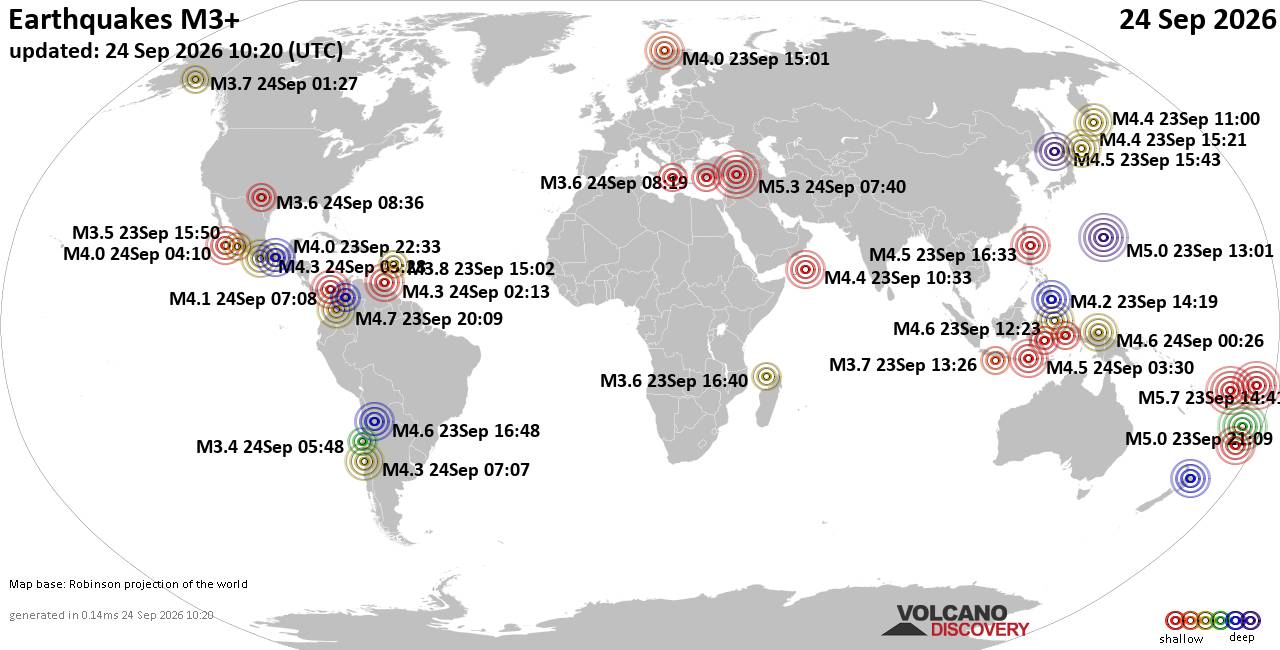
World Earthquake Report for Thursday, 24 September 2026
• Moderate mag. 4.3 earthquake - Madagascar: Mozambique Channel on Thursday, ...
• Small magnitude 3.9 earthquake hits near Hastings, Hastings District, Hawke...
• Volcano earthquake report for Thursday, 24 September 2026
• Light mag. 3.9 earthquake - South Pacific Ocean, 10.2 km south of Hastings,...
• Moderate magnitude 4.1 quake hits 31 miles southeast of Midland, Texas, Uni...
|
|
Forums60
Topics840,728
Posts875,523
Members2,960
| |
Most Online102,106
Jul 10th, 2026
|
|
|
|
|

|