|
|
|
0 members (),
3,669
guests, and
19
robots. |
|
Key:
Admin,
Global Mod,
Mod
|
|
S |
M |
T |
W |
T |
F |
S |
|
1
|
2
|
3
|
4
|
5
|
6
|
7
|
|
8
|
9
|
10
|
11
|
12
|
13
|
14
|
|
15
|
16
|
17
|
18
|
19
|
20
|
21
|
|
22
|
23
|
24
|
25
|
26
|
27
|
28
|
|
29
|
30
|
|
|
|
|
|
|
There are no members with birthdays on this day. |
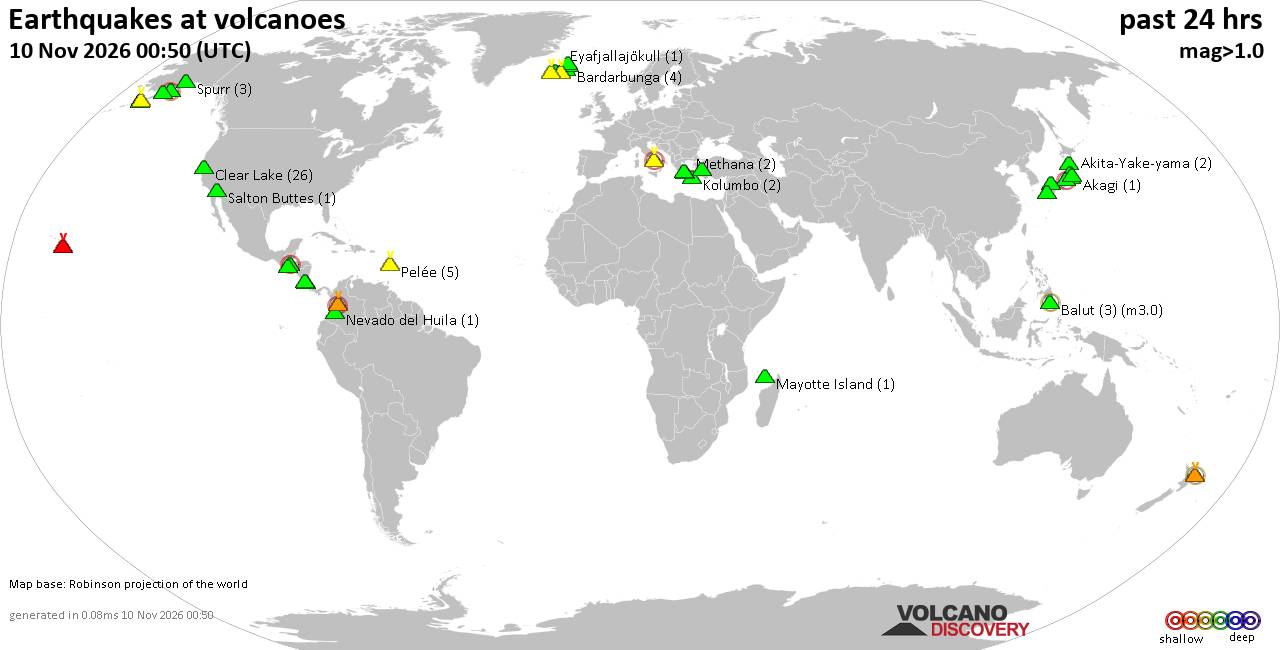
Volcano earthquake report for Tuesday, 10 November 2026
• M -0.6 - 63 km ENE of Pedro Bay, Alaska
• M 0.6 - 47 km ENE of Adak, Alaska
• M 2.3 - 54 km ENE of Susitna North, Alaska
• M 1.4 - 60 km WNW of Nikiski, Alaska
• M 1.1 - 109 km S of McCarthy, Alaska
|
|
Forums60
Topics919,598
Posts954,395
Members2,960
| |
Most Online102,106
Jul 10th, 2026
|
|
|
|
|

|












































