|
|
|
0 members (),
1,590
guests, and
23
robots. |
|
Key:
Admin,
Global Mod,
Mod
|
|
S |
M |
T |
W |
T |
F |
S |
|
|
|
|
|
1
|
2
|
3
|
|
4
|
5
|
6
|
7
|
8
|
9
|
10
|
|
11
|
12
|
13
|
14
|
15
|
16
|
17
|
|
18
|
19
|
20
|
21
|
22
|
23
|
24
|
|
25
|
26
|
27
|
28
|
29
|
30
|
31
|
|
There are no members with birthdays on this day. |
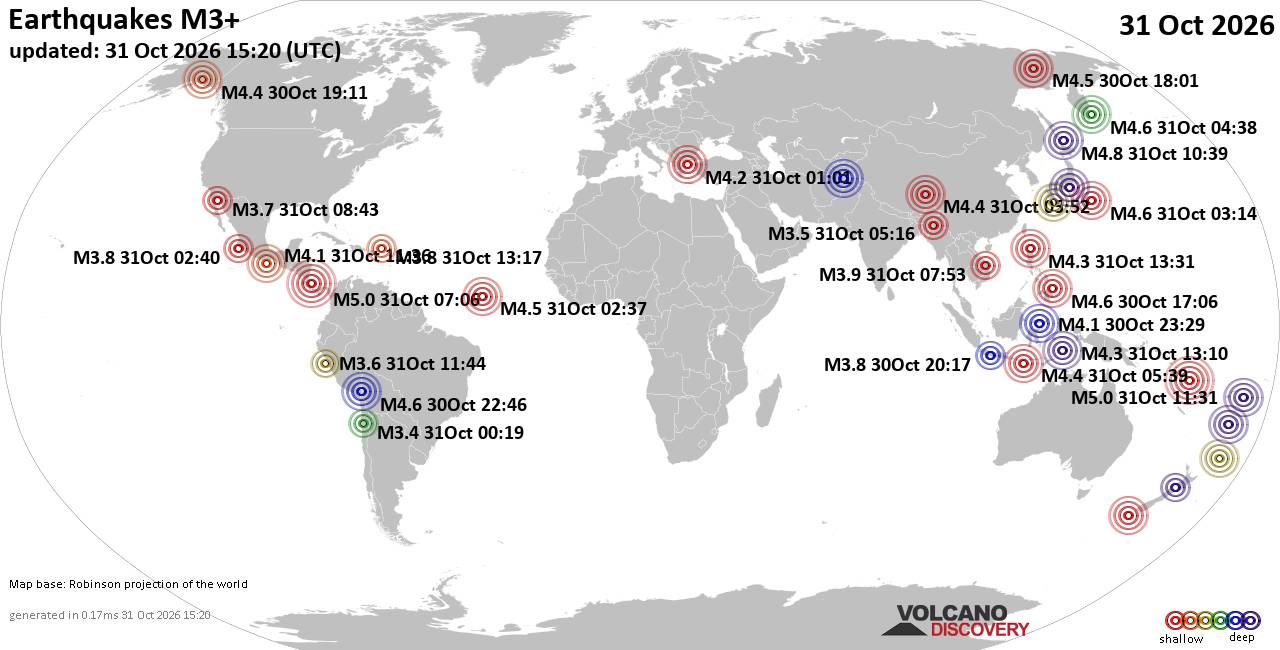
World Earthquake Report for Saturday, 31 October 2026
• M 1.3 - 2 km SSE of Diablo, CA
• M 3.8 - 92 km NE of Cruz Bay, U.S. Virgin Islands
• M 1.8 - 19 km NNW of Ninilchik, Alaska
• M 1.3 - 1 km NE of Diablo, CA
• M 1.3 - 63 km W of Tyonek, Alaska
|

#470618
Thu 22 Sep 2016 03:56:PM
|
Joined: Feb 2001
Posts: 678,977
Launch Director
|
|
Launch Director
Joined: Feb 2001
Posts: 678,977 |
This Metasploit module exploits an Object Injection vulnerability in Kaltura. By exploiting this vulnerability, unauthenticated users can execute arbitrary code under the context of the web server user. Kaltura has a module named keditorservices that takes user input and then uses it as an unserialized function parameter. The constructed object is based on the SektionEins Zend code execution POP chain PoC, with a minor modification to ensure Kaltura processes it and the Zend_Log function's __destruct() method is called. Kaltura versions prior to 11.1.0-2 are affected by this issue. This Metasploit module was tested against Kaltura 11.1.0 installed on CentOS 6.8. Source: Kaltura Remote PHP Code Execution
David Cottle
UBB Owner & Administrator
|
|

CMS The Best Conveyancing solicitors conveyancing quotes throughout the UK
For any webhosting enquiries please email webmaster@aus-city.com
|
|
Entire Thread
|
 Kaltura Remote PHP Code Execution |
Webmaster
|
Thu 22 Sep 2016 03:56:PM
|
|
Forums60
Topics904,155
Posts938,952
Members2,960
| |
Most Online102,106
Jul 10th, 2026
|
|
|
|
|

|