|
|
|
1 members (Alisa),
1,511
guests, and
22
robots. |
|
Key:
Admin,
Global Mod,
Mod
|
|
S |
M |
T |
W |
T |
F |
S |
|
|
|
|
|
1
|
2
|
3
|
|
4
|
5
|
6
|
7
|
8
|
9
|
10
|
|
11
|
12
|
13
|
14
|
15
|
16
|
17
|
|
18
|
19
|
20
|
21
|
22
|
23
|
24
|
|
25
|
26
|
27
|
28
|
29
|
30
|
31
|
|
There are no members with birthdays on this day. |
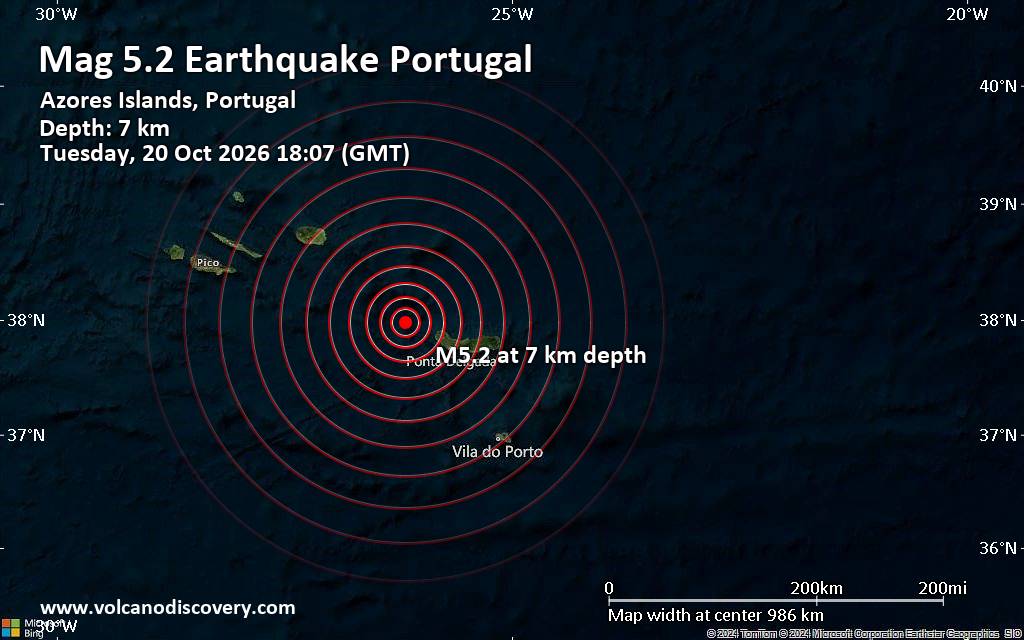
Magnitude 5.2 earthquake strikes near Ponta Delgada, Azores, Portugal
• Possible earthquake reported near Ponta Delgada, Azores, Portugal
• Strong mag. 5.2 earthquake - 10.2 km north of Ponta Delgada, Azores, Portug...
• Magnitude 2.3 quake hits 16 km southwest of Odawara, Japan, early morning
• M 0.4 - 7 km NW of The Geysers, CA
• M 1.9 - 21 km ENE of Denali Park, Alaska
|
|
Forums60
Topics885,285
Posts920,082
Members2,960
| |
Most Online102,106
Jul 10th, 2026
|
|
|
|
|

|