|
|
|
0 members (),
1,936
guests, and
27
robots. |
|
Key:
Admin,
Global Mod,
Mod
|
|
S |
M |
T |
W |
T |
F |
S |
|
1
|
2
|
3
|
4
|
5
|
6
|
7
|
|
8
|
9
|
10
|
11
|
12
|
13
|
14
|
|
15
|
16
|
17
|
18
|
19
|
20
|
21
|
|
22
|
23
|
24
|
25
|
26
|
27
|
28
|
|
29
|
30
|
|
|
|
|
|
|
There are no members with birthdays on this day. |
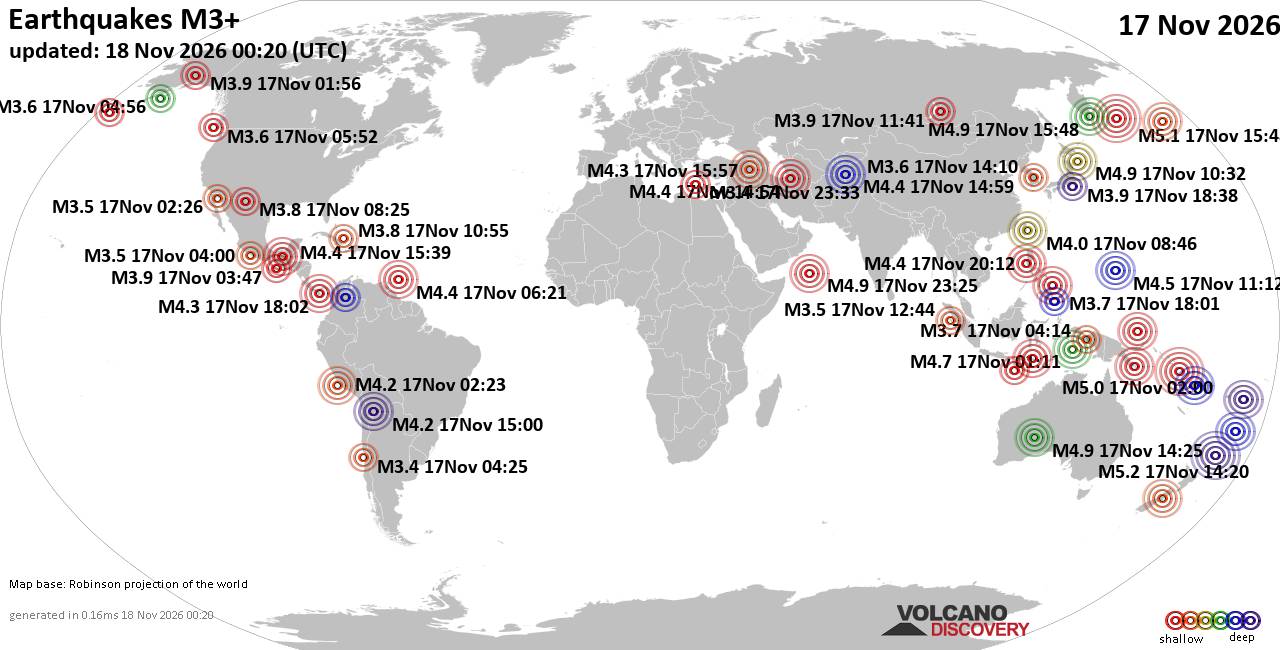
World Earthquake Report for Tuesday, 17 November 2026
• M 2.7 - 89 km ENE of Ouzinkie, Alaska
• M 2.4 - 4 km SW of Madera Acres, CA
• M 2.9 - 13 km SSW of Susitna, Alaska
• M 2.0 - 23 km WSW of Tyonek, Alaska
• M 0.4 - 7 km NW of The Geysers, CA
|
|
Forums60
Topics932,985
Posts967,782
Members2,960
| |
Most Online102,106
Jul 10th, 2026
|
|
|
|
|

|













































